ISO certified by TÜV SÜD
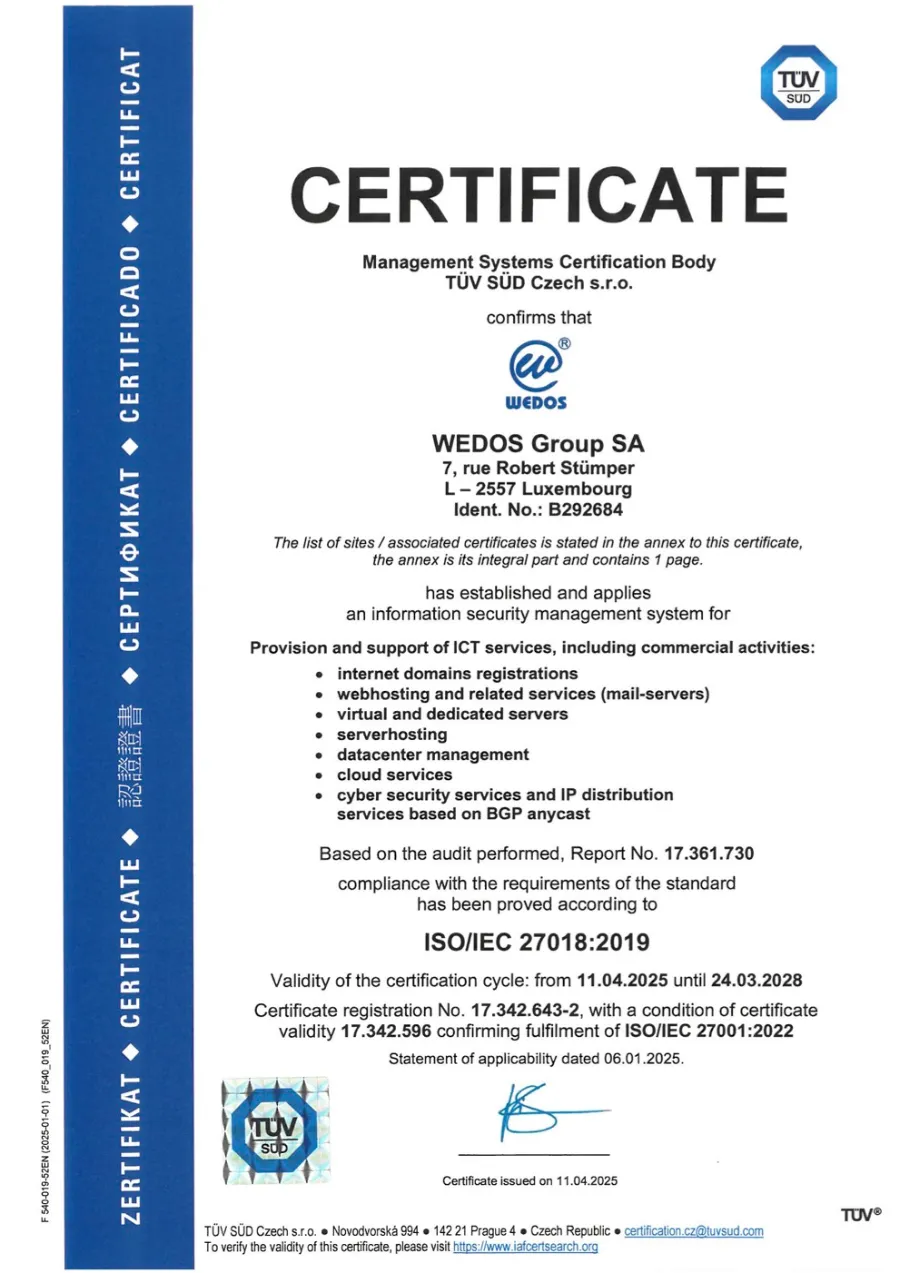
ISO certifications mean that we follow defined processes, not moods. WEDOS Group SA holds five ISO certificates issued by TÜV SÜD Czech, covering quality, the environment, information security and cloud services.
Our certificates at a glance
All certificates are issued to WEDOS Group SA by TÜV SÜD Czech s.r.o., certification body No. 3053, and cover the provision and support of ICT services.
| Standard | Management system | Registration No. | Valid until |
|---|---|---|---|
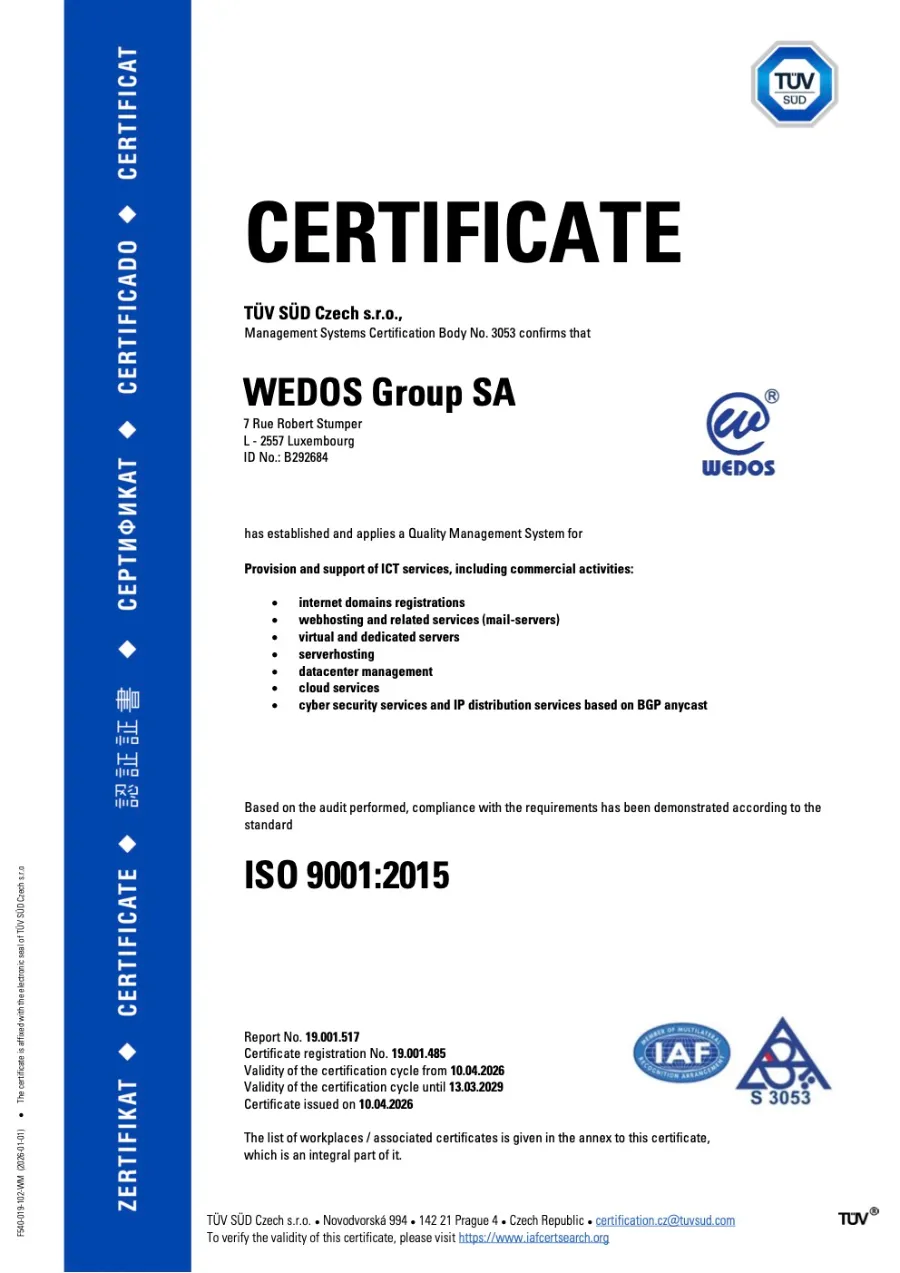
| ISO 9001:2015 | Quality management | 19.001.485 | 13 March 2029 |
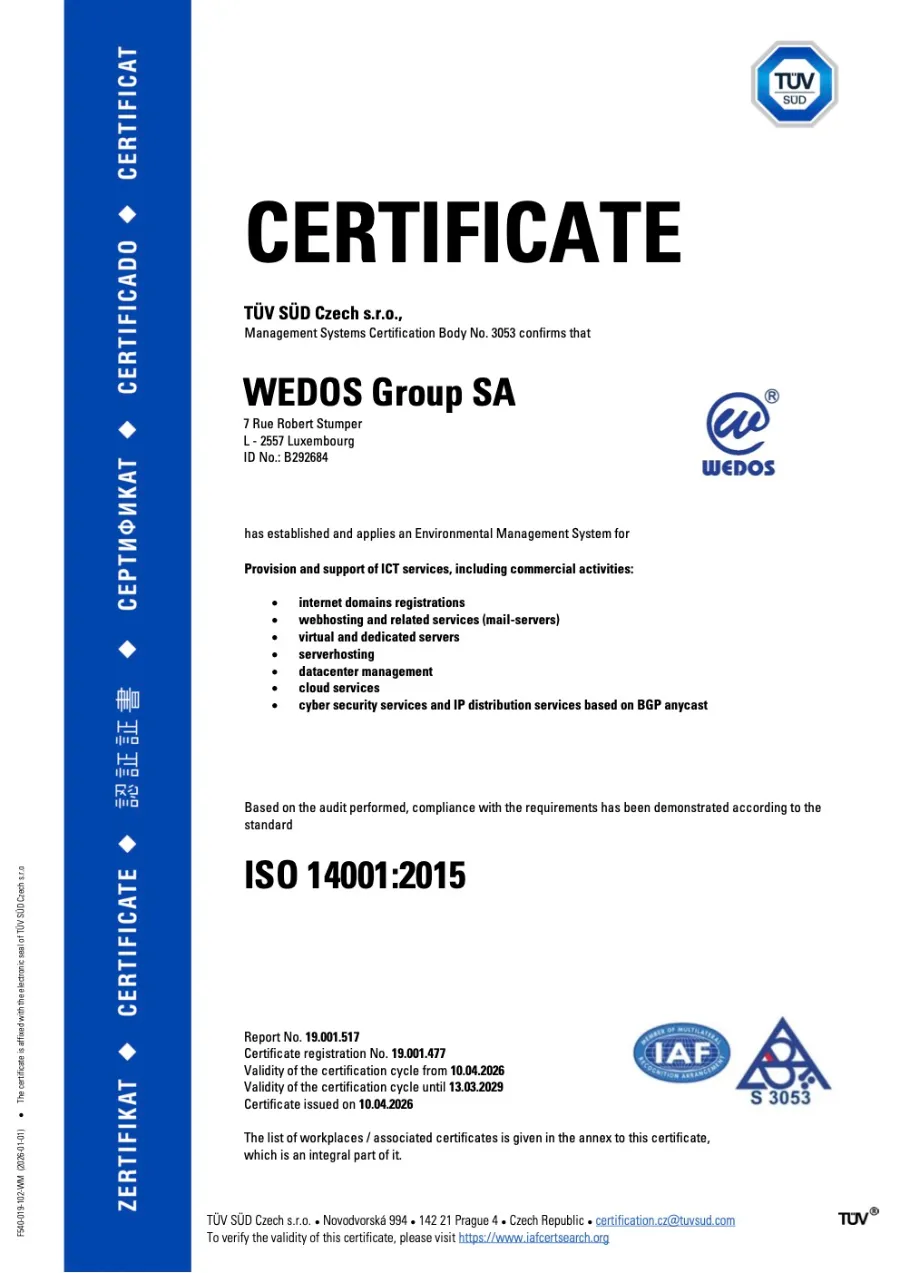
| ISO 14001:2015 | Environmental management | 19.001.477 | 13 March 2029 |
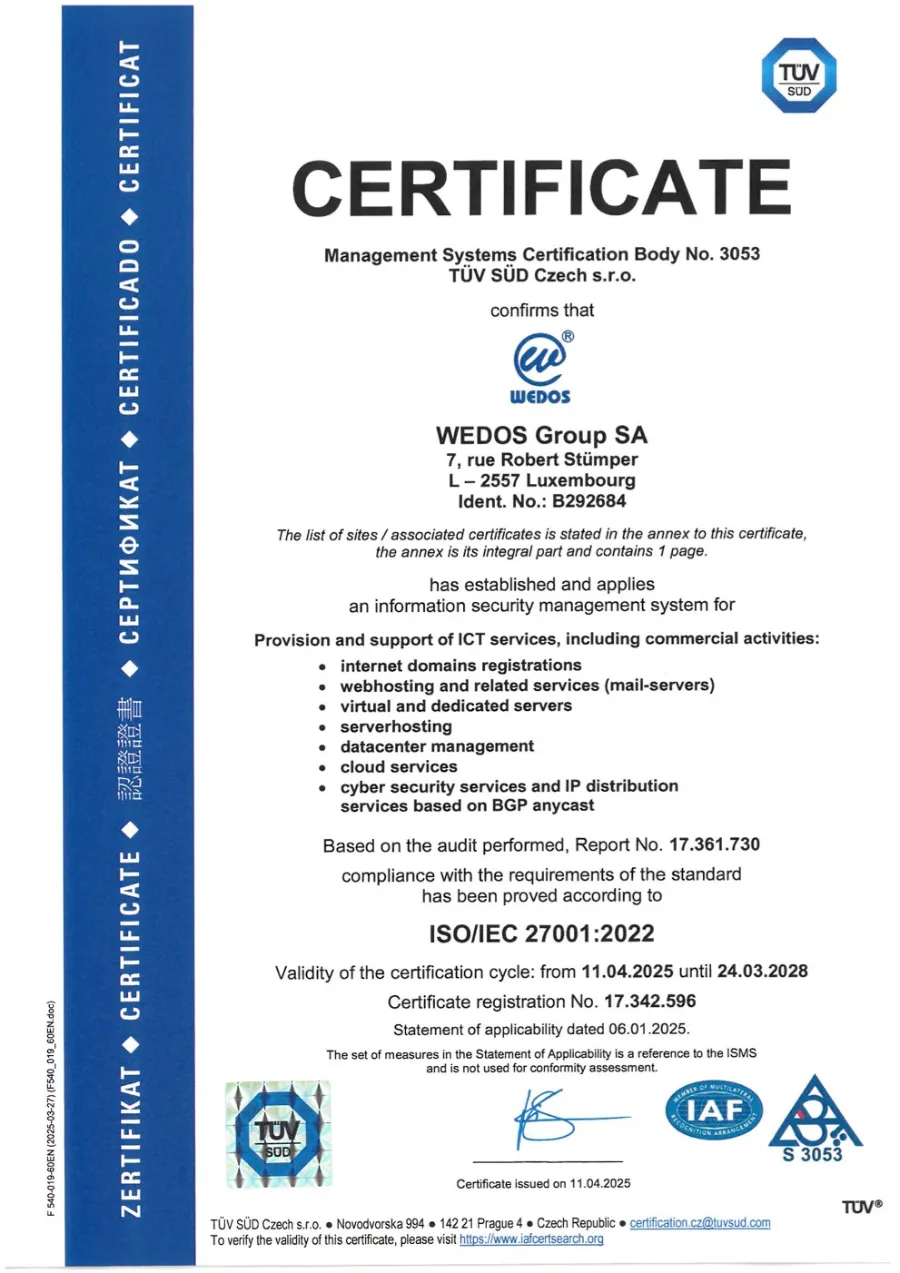
| ISO/IEC 27001:2022 | Information security | 17.342.596 | 24 March 2028 |
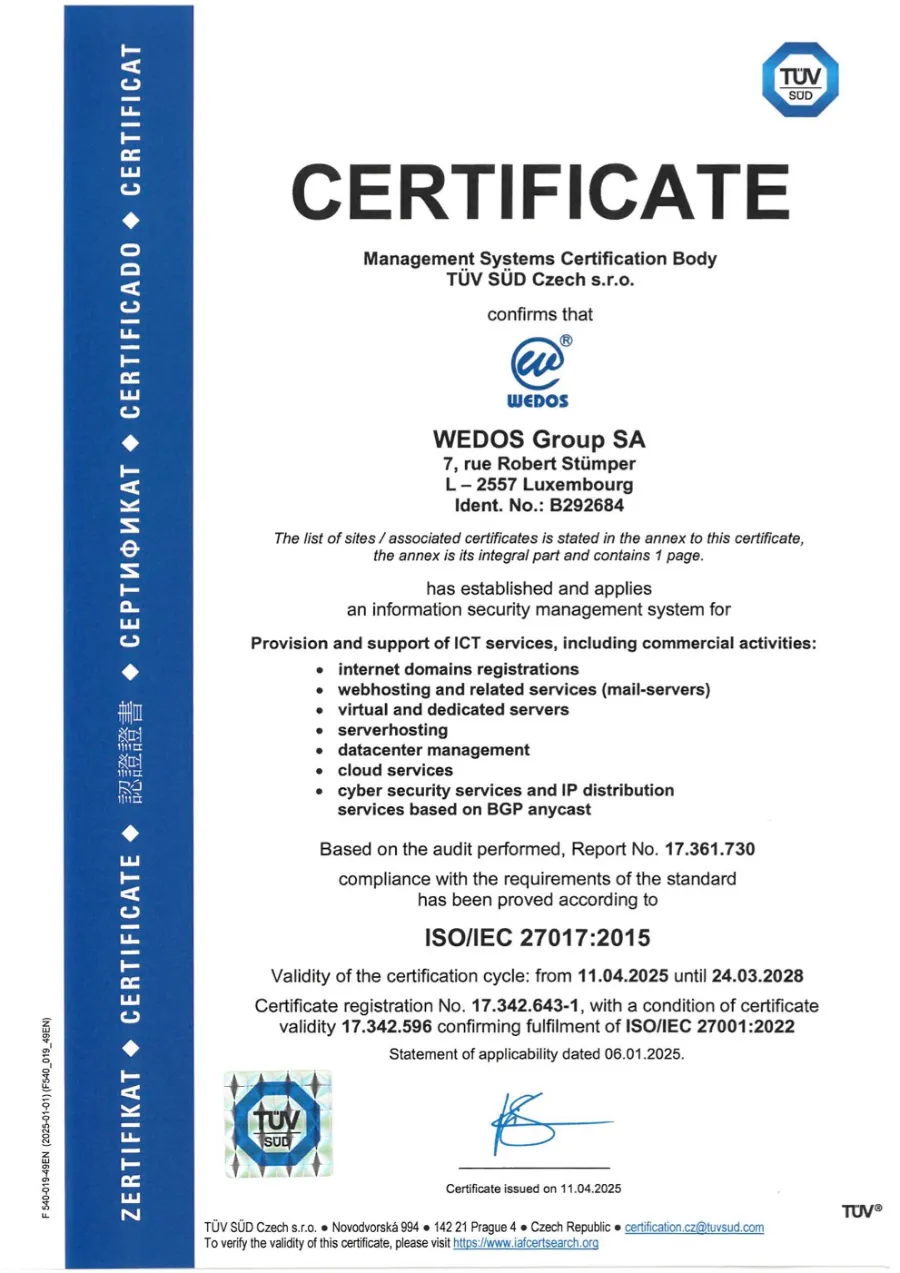
| ISO/IEC 27017:2015 | Information security for cloud services | 17.342.643-1 | 24 March 2028 |
| ISO/IEC 27018:2019 | Protection of personal data in public clouds | 17.342.643-2 | 24 March 2028 |
You can verify any certificate in the IAF CertSearch database at iafcertsearch.org.
ISO 9001:2015: Quality management
It guarantees a stable and unchanging quality of the services we provide.
- The whole company and all its processes are based on compliance with legal standards.
- All internal processes and activities have their own guideline based on predefined rules.
- We have preventive measures in place to avoid defects and outages of the services we provide.
ISO 14001:2015: Environmental management
It proves our positive attitude to the environment.
- We take environmental protection and the prevention of environmental damage seriously.
- All our steps aim to minimise the environmental impact of our activities.
- We prevent any damage to the environment.
ISO/IEC 27001:2022: Information security
It demonstrates that we can systematically identify and minimise information security risks.
- We have continuity management plans for human or natural emergencies.
- We protect confidential information better and reduce the risk of hacker attacks.
- We cope faster with the consequences of an attack and keep improving how we recover from emergencies.
- We use a structured, globally recognised information security methodology.
- We comply with legal and contractual requirements.
ISO/IEC 27017:2015: Cloud security
A set of procedures that maintain information security for cloud services. It extends ISO/IEC 27001.
- Defines roles and responsibilities within the cloud environment.
- Provides clear and safe rules for removing all data from the cloud.
- Provides rules for separating customer services in the virtual environment.
- Defines both software (cloud) and hardware (physical) security.
- Defines how cloud services are monitored.
ISO/IEC 27018:2019: Personal data in the cloud
A set of procedures that protect personally identifiable information in public clouds. It extends ISO/IEC 27001.
- Provides greater security of personal data and information.
- Guarantees transparency in the use of personal data.
- Sets rules for passing data to subcontractors.
- Meets all legal standards.
Certified since 2011
-
2011: ISO 9001 and ISO 14001
Quality and environmental management. We chose them because we care about the environment, which is also why we buy energy-efficient processors for our servers.
-
2013: ISO/IEC 27001
Information security management: a systematic approach to confidential information, covering people, processes, IT systems and corporate strategy.
-
2021: ISO/IEC 27017 and 27018
Two cloud-focused extensions of ISO/IEC 27001, one of the first in the Czech Republic: information security for cloud services and protection of personal data in public clouds.

Need documents for a tender or an audit?
Our Security & Compliance page collects the SLA, the data processing agreement and other documents in one place.